
Artificial intelligence (AI) is moving beyond content generation and recommendations towards systems capable of carrying out multistep tasks across connected workflows. In packaging operations, Agentic AI Tools could support artwork preparation, approval routing, document checks and the coordination of production information. However, allowing software to perform these tasks introduces a governance question: which actions can an agent execute independently, and which decisions must remain under human control? The answer depends on the task, the consequences of an error and the permissions granted to the system. As packaging workflows become more connected, businesses need to define these boundaries before delegating operational responsibilities.
Defining Responsibility Before Delegating Workflow Tasks
Unlike conventional automation that follows predefined rules, agentic systems can use available tools and information to pursue objectives through multiple steps. This creates different risks when an agent can interact with business systems rather than simply generate a suggestion. The National Institute of Standards and Technology (NIST) has identified agent identity, authorisation and security as important areas for developing trustworthy AI agent systems. For packaging teams, Agentic AI Tools therefore require controls that connect technical permissions with business responsibilities. An agent that summarises a design brief does not need the same authority as one that modifies approved artwork or initiates a production release.
Decisions that Need Clear Boundaries
-
Task Authority: Define which actions an agent may perform independently, such as organising documents, identifying missing information or preparing a draft for review.
-
Approval Rights: Establish which decisions require explicit human authorisation, particularly changes to approved artwork, product information or production files.
-
Accountability: Assign responsibility for configuring, monitoring and reviewing agent activity. Delegating a task to software does not remove the organisation’s responsibility for the resulting workflow.
-
Exception Handling: Define what happens when instructions conflict, required information is missing or an agent produces an unexpected result. The system should have a clear escalation route rather than proceeding without appropriate checks.
These boundaries should reflect the actual capabilities of the system and the potential consequences of its actions. Agentic AI Tools may support routine coordination, but their authority should not extend automatically to every connected application or business decision. Packaging teams need to distinguish between tasks that can be delegated, actions that require validation and decisions that must remain with an authorised person. Establishing these distinctions provides the foundation for more accountable AI adoption without assuming that every task requires the same level of supervision.
Permissions and Controls Must Match the Task
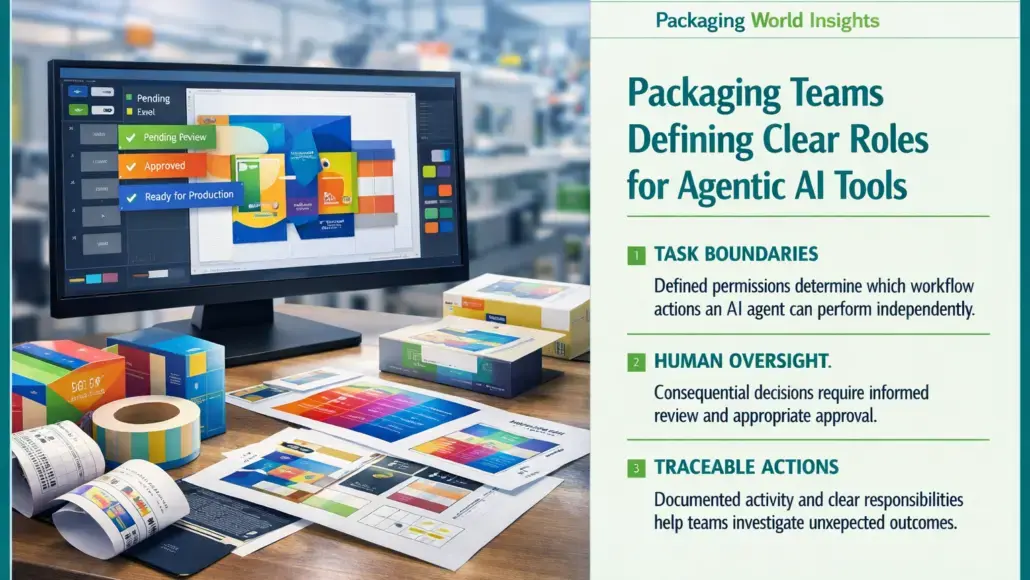
The authority assigned to Agentic AI Tools should reflect the potential consequences of their actions, rather than the number of tasks they can complete. In packaging workflows, preparing a draft proof presents a different level of risk from modifying approved artwork or releasing a production file. The Open Worldwide Application Security Project (OWASP) identifies excessive permissions, misuse of tools and cascading failures among the risks associated with agentic applications. Packaging businesses should therefore restrict system access, validate consequential actions and establish clear escalation procedures. Controls must be built into the workflow rather than relying exclusively on written policies or the assumption that an agent will always follow its instructions.
Defining Agent Permissions
-
Task boundaries: Specify the applications, files and actions the agent is authorised to access or perform.
-
Restricted authority: Prevent routine workflow permissions from automatically extending to final artwork approval or production release.
-
Action validation: Check outputs and proposed changes against defined requirements before consequential actions are executed.
-
Traceability: Maintain suitable records of actions, approvals and exceptions so that teams can investigate unexpected results.
Human Oversight Must Carry Real Authority
Governance also requires clarity about who supervises the system and who remains responsible for its outcomes. The National Institute of Standards and Technology’s Artificial Intelligence Risk Management Framework emphasises organisational accountability, risk assessment and ongoing management. Applied to packaging, this means appointing responsible workflow owners, defining approval thresholds and ensuring reviewers have sufficient information to evaluate an agent’s decisions.
Agentic AI Tools should escalate uncertain or conflicting cases rather than proceeding beyond their permitted scope. Human oversight must also include the ability to intervene, suspend an inappropriate action or revoke access when necessary. A recorded approval alone is insufficient if the reviewer cannot understand the decision or challenge the proposed action.
Making Oversight Operational
-
Named responsibility: Identify who owns the workflow, monitors performance and handles exceptions.
-
Meaningful approval: Require informed human authorisation for high impact decisions involving approved artwork, product information or production release.
-
Incident escalation: Define how teams respond to unexpected actions, compromised access or repeated validation failures.
-
Ongoing review: Reassess Agentic AI Tools as their capabilities, connected systems and operational risks change.
These controls help organisations delegate appropriate tasks while retaining accountability for business critical decisions.
Making Accountability Part of Packaging Workflow Design
Responsible adoption requires packaging businesses to define decision rights before delegating tasks to Agentic AI Tools. Clear permissions, proportionate human approval and traceable actions help teams distinguish routine automation from decisions that could affect approved artwork, product information or production release. Governance should also specify who reviews exceptions, investigates failures and intervenes when a system acts outside its authorised scope.
Governance Priorities
- Restricted permissions: Limit access and actions to the system’s assigned responsibilities.
- Human accountability: Preserve informed oversight for decisions with significant operational consequences.
- Ongoing monitoring: Review system behaviour, exceptions and permissions as workflows evolve.
The effectiveness of these controls also depends on whether employees can interpret AI outputs, identify errors and intervene appropriately. This makes digital production skills an important next consideration. Delegating tasks to AI does not eliminate the need for capable people; it changes the judgement and oversight their roles require.
References
- National Institute of Standards and Technology – Artificial Intelligence Risk Management Framework (AI RMF 1.0) – 2023.
- OWASP GenAI Security Project – OWASP Top 10 for Agentic Applications – 2025.